Introduction
The rapid growth of autonomous AI agents has made local trace capture a standard debugging practice. However, capturing execution logs is only half the problem ensuring those traces can be shared without exposing sensitive data is the real challenge. AgentInspect, an open-source TypeScript toolkit, introduces a safety model designed to bridge that gap.
What Happened
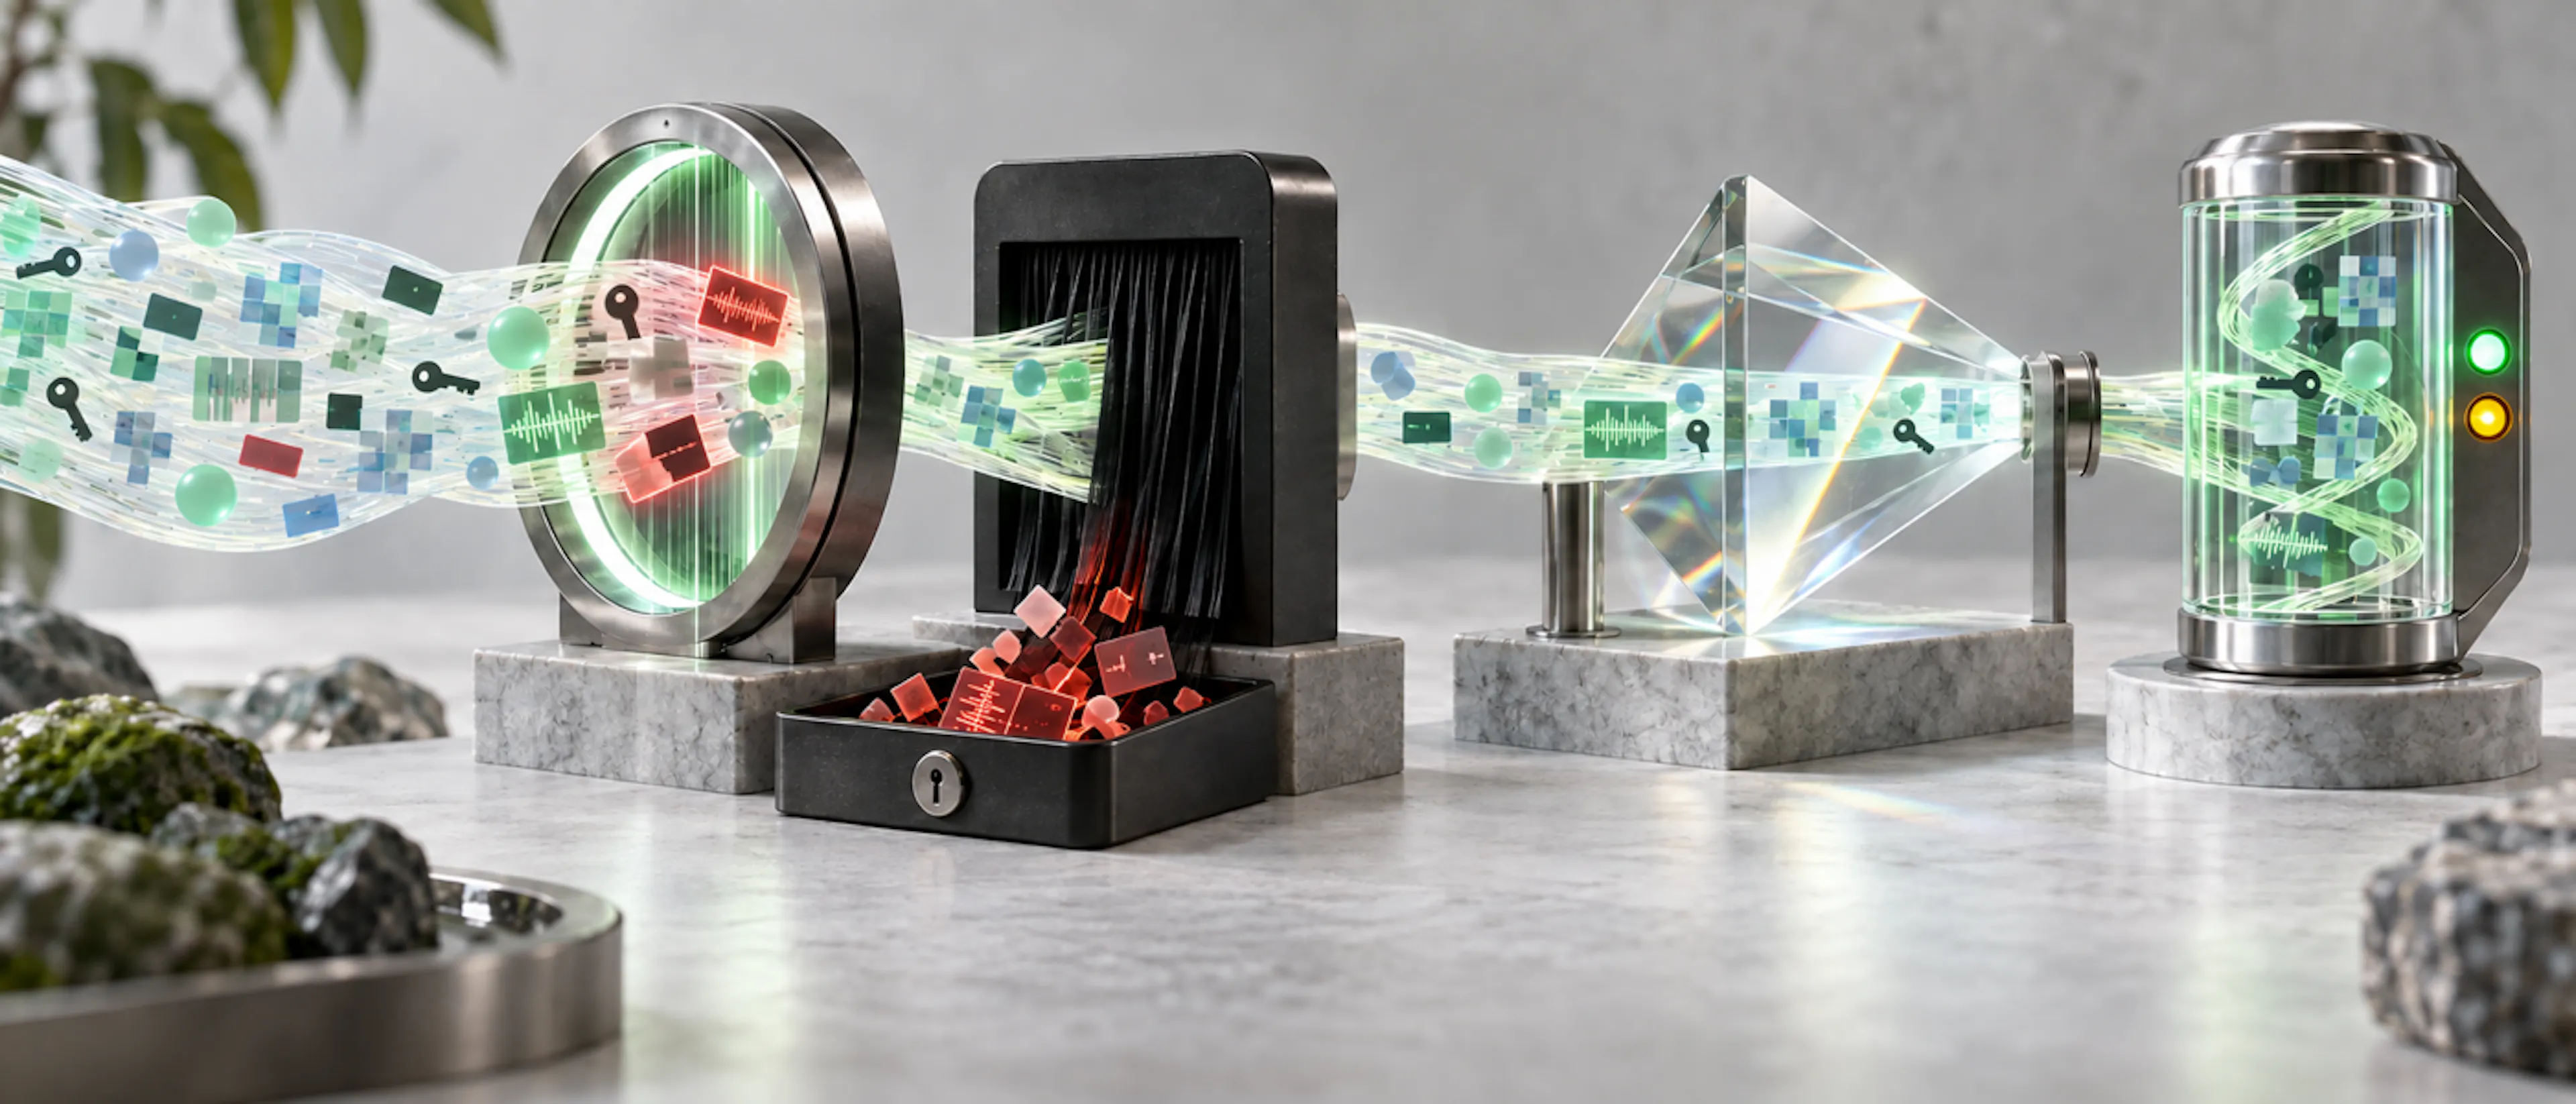
The article outlines a structured evidence lifecycle that moves from raw capture to share-ready artifacts. Central to this model is the distinction between source risk and artifact risk: a trace may be local-safe but still contain fields inappropriate for public sharing. AgentInspect provides CLI-driven safety checks, redaction profiles, and bundle creation to make this process transparent and auditable.
The workflow unfolds in stages: source assessment, redaction to a separate artifact, post-redaction evaluation, bundle packaging, and integrity verification. Each stage answers a specific question about what risks remain and whether the evidence is fit for its intended context.
Why This Matters
AI traces frequently contain prompts, model outputs, tool arguments, retrieved documents, URLs, identifiers, and occasionally credentials or personal data. Simply because a system is local-first does not eliminate the responsibility to inspect what was captured. The framework emphasizes that redaction does not equal safety if a custom identifier slips through, the derived artifact inherits that risk.
Beyond the tool itself, the article situates the problem within broader data governance concerns. References to OWASP logging guidance and NIST log-management frameworks position the approach as part of a larger organizational strategy for handling sensitive telemetry responsibly.
Key Takeaways
- Assess before you share. Understand what the original trace contains before producing any artifact.
- Redact into a separate file. Never modify the source trace in place; keep the original restricted while producing a derived candidate for sharing.
- Verify the artifact. Run post-redaction safety checks; a green status does not guarantee universal compliance.
- Bundle with integrity checks. Use the manifest and SHA-256 hashes to confirm that shared files match the intended evidence package.
- Human review remains essential. Automation surfaces warnings and unknowns, but final sharing decisions require judgment.
Conclusion
AgentInspect's safety model does not claim to certify privacy, security, or regulatory compliance. Instead, it makes the stages of evidence handling explicit: capture choices, redaction rules, artifact inspection, access controls, and reviewer judgment all contribute to safe sharing. The tool's best-effort detectors help surface common risks, its status model preserves warnings rather than masking them, and its bundles enable integrity verification, with none replacing human accountability. In practice, safe evidence emerges from deliberate capture, thoughtful redaction, and context-aware sharing, not from a single command.



Discussion
Join the conversation
Thoughtful reactions, questions, and follow-up ideas help shape the next story.