Introduction
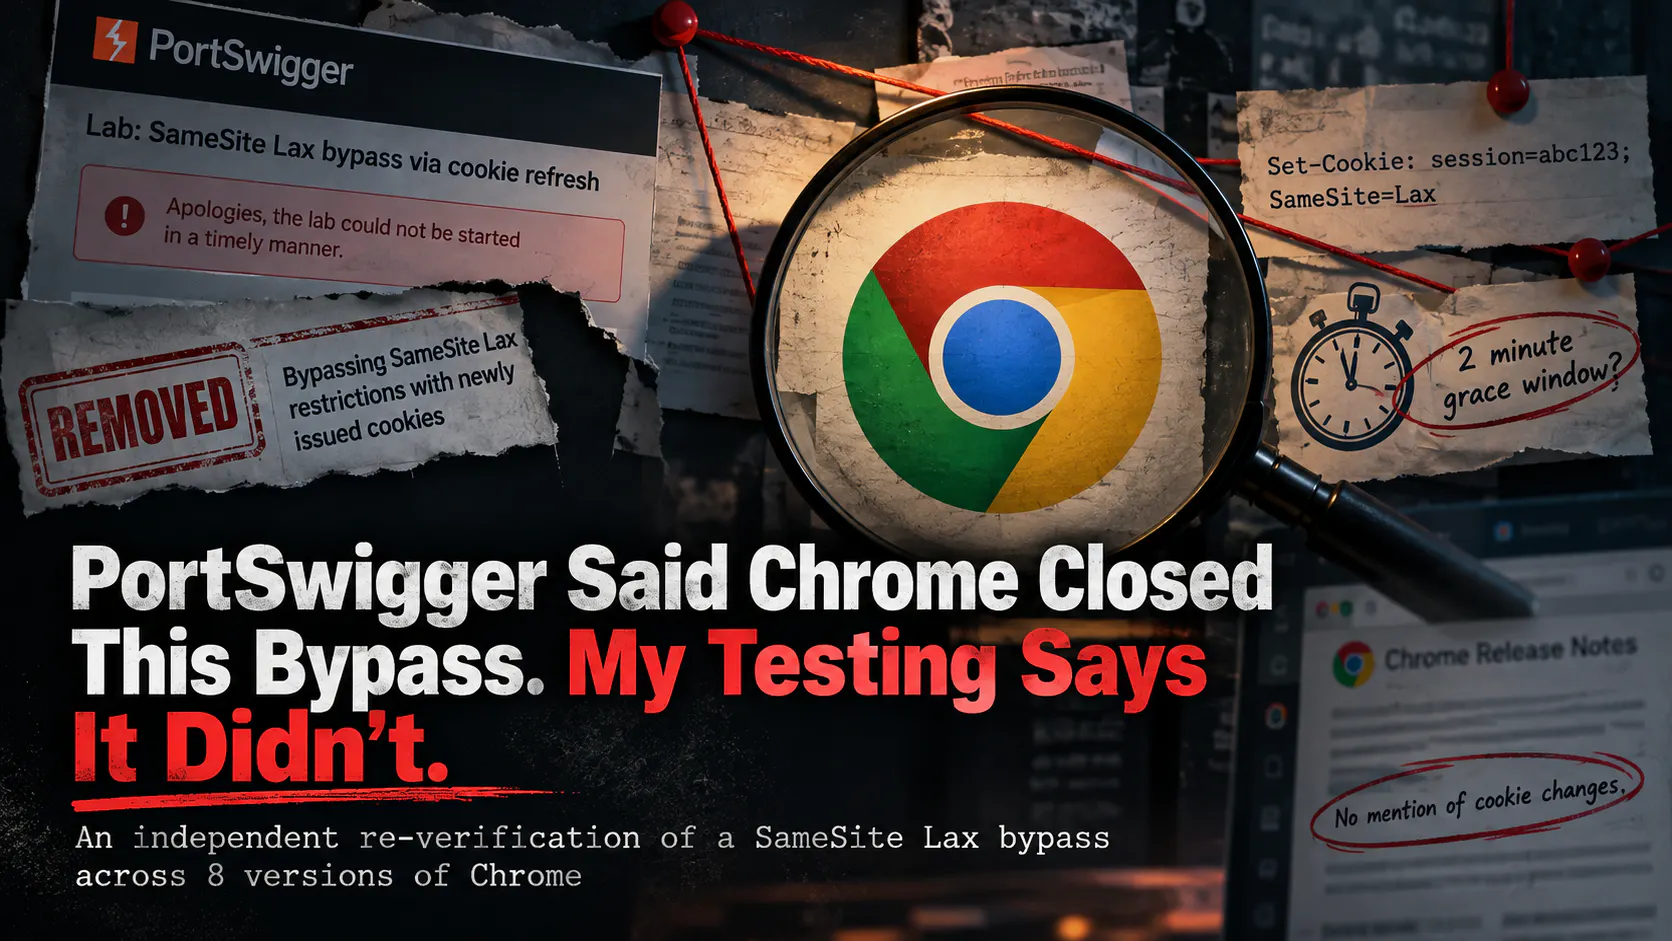
PortSwigger removed its CSRF lab and theory section claiming Chrome updates broke the bypass. A security researcher decided to test the vulnerability independently.
What Happened
On August 11 2026 the SameSite Lax bypass via cookie refresh lab stopped launching. PortSwigger support attributed the issue to recent Chrome updates specifically version 150 and quietly removed both the lab and the theory section Bypassing SameSite Lax restrictions with newly issued cookies from the Academy.
Why This Matters
The removed section detailed a two minute grace period Chrome grants to cookies issued without an explicit SameSite attribute. The researcher built a two site Python proof of concept and tested the bypass across eight Chrome versions from 141.0.7340.0 to 155.0.8059.40. Every test confirmed the vulnerability remains active in current builds.
Key Takeaways
The lab and theory section were removed without a public Chrome changelog confirming the change. Independent testing across eight Chrome versions confirms the SameSite Lax bypass via cookie refresh still works. The two minute grace window for default Lax cookies remains functional. Researchers should verify claims rather than accept platform changes at face value. PortSwigger has not publicly explained the removal and the vulnerability's continued existence raises questions about academy content maintenance.
Conclusion
When a security platform removes content citing browser changes independent verification is the only way to know if the flaw persists. The authors hands on testing across multiple Chrome builds shows the CSRF bypass via SameSite Lax cookie refresh is still active. This case underscores a broader principle curiosity and self testing often reveal truths that official updates may obscure.



Discussion
Join the conversation
Thoughtful reactions, questions, and follow-up ideas help shape the next story.